-
This is an opsec guide for crypto cold storage.
-
Opsec is a lifelong journey; there is no complete and final solution. Protect yourself at all times.
-
Your opsec strategy must be appropriate to the threat model. More money or illegal operations = more risk.
-
Impeccable opsec is easiest for Monero, and hardest (although technically possible) for interaction with certain smart contracts.
-
I will be working on software to fill in the gaps to make this method as convenient as possible (for my needs and maybe yours too).
-
This guide assumes familiarity with basic cryptocurrency concepts like private keys, nodes, transactions, bitcoin, monero, smart contracts.
-
This guide does not contain technical implementation guidance because that would make it too long.
-
This guide does not mention physical security. Situational awareness is essential.
-
If you have any questions please ask.
-
AI free guide.
-
I'm not an authority on anything. Think for your fucking self!
-
This method is for saving money / long term storage / investment / high value trading accounts. Not day to day transactions.
Contents
Foundation
Layer 1- Physical Entropy Keys
Layer 2- Cold Device
Layer 3- Air Gap
Layer 4- Decoy and Activation Keys
Trust
Layer 5- Trusted Software
Layer 6- Trusted Swaps
Pseudonymity
Layer 7- Protected IP
Layer 8- Compartmentalization
Foundation:
Physical Entropy Keys:
- As we saw with the Coldcard exploit, your wallets are only as secure as the entropy (randomness) used to generate the seed.
- Generating this entropy computationally might be vulnerable to exploits, and is impossible to conclusively verify.
- The surest way to get secure keys with sufficient entropy is to manually generate entropy by rolling dice.
- 99 dice rolls contains enough entropy for a secure 24 word seed phrase (using words from the BIP-39 word list)
Cold Device:
- If your private keys are ever exposed to any device connected to the internet, then they might be stolen by software exploits.
- Only expose your keys to hardware that has had its radio's physically removed.
- Never use hardware that is specifically sold for crypto cold storage.
- Run tails to minimize the risk of private keys being recoverable from your hardware between sessions.
Air Gap:
- Signing and broadcasting transactions requires some communication between your cold device and an internet connected device.
- It is therefore an unavoidable risk that a software exploit might leak your keys in this communication.
- To minimize the attack surface, and to make the process fully auditable, all communications must use QR codes and never wires or radios (wifi/Bluetooth).
- To update the cold device, use a fresh memory stick every time to prevent the stick itself from leaking your keys.
- For Monero, this is easy using Feather Wallet on both devices.
- For Bitcoin, its even easier using Sparrow Wallet on both devices.
- Other blockchains lack convenient support for this but I am working on support for certain chains.
Decoy and Activation Keys:
- All crypto custodians are vulnerable to wrench attacks, where an attacker uses violence to coerce them into revealing keys.
- Multi-sig wallets allow the custodian to guarantee the safety of their money, but might do nothing to stop the violence; is it worth getting tortured to death because your attacker does not trust that you can't access the money anyway?
- The best defense is obviously to avoid being a known, easy or valuable target. However, the vulnerability cannot be eliminated.
- Sometimes a wrench attack stops upon discovery of a decoy wallet (with decoy funds); you keep your money, life and some teeth.
- There is a convenient way to store your keys which is both easy to manage and allows you to surrender your cold device if coerced and only lose your decoy wallet.
- For every crypto that you want, store the keys for decoy wallets on your tails stick. These might change over time.
- Store one master key on paper. This is inputted when making transactions, but should never be digitally stored.
- Use a software to multiply the master key with each of your decoy wallet keys to derive your actual wallet keys.
Trust:
Trusted Software:
- Even despite maintaining an impeccable air gap, it is possible for compromised wallet software to leak your seed through qr codes, or to sign fraudulent transaction.
- This risk is avoided using highly reputable, open source and extensively audited software.
- If your write your own software, it is essential to follow supply chain best practices during installation.
- If you use existing software, it is essential to verify hashes against multiple official sources to guarantee legitimacy.
Trusted Swaps:
- When interacting with any swap, there is the potential to lose funds.
- When interacting with any smart contract, there is the potential for your entire account to be drained.
- Split funds into different accounts if interacting with complex smart contracts.
- Limit the amount of money transmitted in any given swap.
- Use the most reputable, open source and extensively audited swap services.
- Prefer permissionless swaps where possible (like thorchain) and otherwise prefer no KYC swaps.
- It is not unlikely that KYC swaps will leak your information to wrenchers.
Pseudonymity:
Protected IP:
- If you IP address is associated with your onchain identity then you are a good target for wrenchers.
- Using a VPN alone is not sufficient protection because you cannot verify that they don't keep logs.
- Using Monero over tor is the easiest solution.
- Using other cryptos over tor is more complicated and often requires communicating with public nodes that expose tor endpoints.
- Be careful not to expose your identity by using public blockchain explorers.
Compartmentalization:
- There is always a high risk that your onchain identity is tracked, connected to your IP address, or otherwise connected to your person.
- This is useful for both government and criminal adversaries.
- The impact of this risk can be limited by compartmentalization: using different isolated accounts for different funds at different times.
- This is achieved using Monero!
- Once per year (for example) use all your crypto to buy monero.
- Then use monero to buy back your cryptos, one by one, keeping the transactions isolated.
- Be vigilant to prevent metadata from revealing links between accounts, for example by temporal/cluster analysis or digital fingerprinting.
- This prevents your accounts from being associated with each other or tracked across time.
- You have the option to leave behind apparent losses to support an alibi of lost funds; 'lost it all on nfts and memecoins' might be more believable than 'boating accident'.
Bonus security tip:
VeraCrypt Tentacle Porn:
- It would be better that nobody knows you have cold storage hardware or software at all.
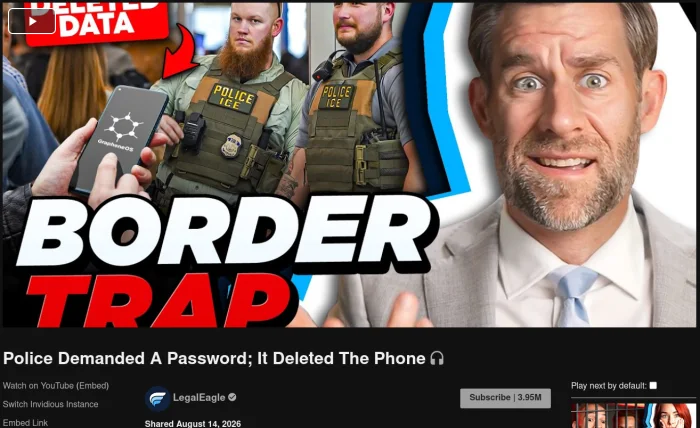
- If you are worried about your tails stick being seized by police and being forced to reveal the password, there is a special method to avoid further suspicion.
- Use VeraCrypt to put an encrypted data partition on the stick, containing all the cold storage software and decoy keys.
- VeraCrypt can be configured so that a second password decrypts a second data volume containing something else, and the primary data volume is hidden but not destroyed. (a miracle of encryption)
- The hidden data volume should be embarrassing or incriminating, to justify being hidden on an encrypted stick, but nothing to do with crypto.
- For example, put mountains of tentacle porn and other fetish material, and act all embarrassed when its discovered.
- Now they think you're a paranoid pervert rather than a crypto custodian. They'll have a good laugh, diffuse the tension of suspicion and you can move on.
Summary
- Keep your private keys secure.
- Beware of wrench attacks and software exploits.
- Stack redundant security measures to minimize risks.
- Minimize reliance on trust.
- Use decoys as the final layer of defense.
Thankyou for reading :D
Signature
You are the only light
blog: freedomthemoon.netlify.app
game: evoverse.onrender.com
UK GIS: https://pub-6199d7cd0f754c4f8987b0455ceb6161.r2.dev/index.html
github: moonboi420